Ticket fraud costs the live events industry an estimated $12 billion annually. Counterfeit tickets, duplicated barcodes, and secondary market scams leave fans stranded at venue doors and organizers dealing with chargebacks. The root of the problem is surprisingly simple: static QR codes are fundamentally insecure. Once someone has a screenshot of your ticket, they have your ticket.
At Mega Tickets, we took a different approach. We built a rotating QR code system from the ground up — one that makes ticket fraud mathematically impossible. Here is how it works, why it matters, and how it compares to every other ticketing platform on the market.
The Problem With Static QR Codes
A traditional ticket QR code is just a string of text encoded into an image. That string might be something like TICKET-29384-VIP-SEAT12. Once generated, it never changes. This creates three critical vulnerabilities:
- Screenshot sharing: Anyone who sees your QR code — in a text message, on social media, or over someone's shoulder — can copy it. The first person to scan it at the door gets in. The legitimate buyer does not.
- Counterfeit duplication: Scammers buy one real ticket, extract the QR code, and sell copies to dozens of people. Only one scan works. Everyone else is turned away.
- Secondary market abuse: Scalpers purchase tickets in bulk and resell at inflated prices using the same static codes, with no way for the organizer to verify chain of custody.
Platforms like self-serve platforms and industry-average platforms have tried to address this with PDF tickets and basic barcodes, but the fundamental flaw remains: if the code does not change, it can be copied.
How Mega Tickets Rotating QR Codes Work
Our system generates a new QR code every 30 seconds. Not a new image of the same data — a completely new cryptographic token that is valid for exactly one 30-second window and can only be generated by the authenticated ticket holder's device.
The Technical Architecture
Here is the step-by-step process:
- Ticket purchase
When a user buys a ticket, our server generates a unique secret key for that ticket. This key is stored server-side and encrypted on the user's device. It never appears in the QR code itself.
- Code generation
Every 30 seconds, the app combines the secret key with the current Unix timestamp (rounded to 30-second intervals) using HMAC-SHA256 — the same algorithm used in banking two-factor authentication. The result is a one-time token.
- QR encoding
The token, along with a ticket identifier and a timestamp, is encoded into the QR code. The code is visually different every 30 seconds.
- Validation at the door
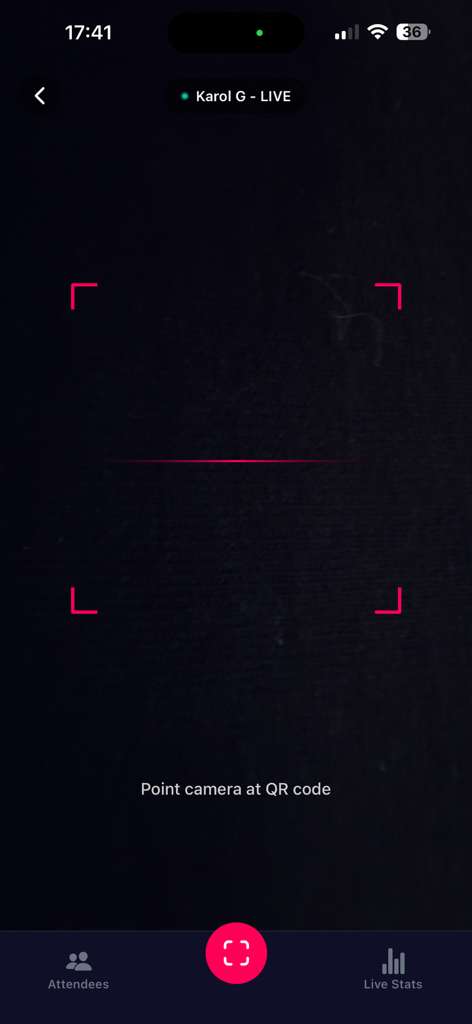
The scanner app sends the token to our server, which independently generates the expected token using the same secret key and timestamp. If they match and the ticket has not already been scanned, entry is granted.
The mathematical guarantee is this: without the secret key stored on the original device, it is computationally infeasible to generate a valid token. Even if someone photographs the QR code, it expires in 30 seconds and cannot be reverse-engineered to produce the next code.
GPS Gating: The Second Layer
Rotating codes alone prevent screenshot fraud. But we added a second layer to prevent another attack vector: remote code sharing. Without GPS gating, someone could share their screen in real-time with a friend at the venue, who could scan the constantly updating code on their behalf.
Here is how GPS gating works:
- Geofence activation: When the event is within 2 hours of starting, the QR code screen only activates when the user's device is within a configurable radius of the venue (typically 500 meters).
- Location hash: The device's GPS coordinates (rounded to reduce precision concerns) are included in the HMAC calculation. The server verifies that the code was generated from a device physically near the venue.
- Privacy-first: We do not store precise location data. The GPS coordinates are hashed and discarded after validation. We know the user was near the venue; we do not know their exact position or track them afterward.
This means even a live screen share is useless. The code generated from a device 10 miles away will not pass the server's geofence validation.
Static vs. Rotating: A Direct Comparison
| Feature | Static QR (self-serve platforms, etc.) | Rotating QR (Mega Tickets) |
|---|---|---|
| Code changes | Never | Every 30 seconds |
| Screenshot protection | None | Full — expired in 30s |
| Duplication prevention | None | Cryptographic — HMAC-SHA256 |
| GPS gating | Not available | 500m geofence |
| Offline support | Yes (static image) | Yes (pre-cached tokens) |
| Scalper resistance | Low | Very high |
| Real-time validation | Basic scan | Cryptographic + location |
What About Offline Scenarios?
A common concern with rotating codes is connectivity. What happens if the attendee's phone has no signal at the venue? We designed for this from day one.
When the user opens their ticket within range of the venue, the app pre-generates the next 20 minutes of tokens (40 codes) and caches them locally. The scanner can validate these tokens against a locally synced copy of the event's validation rules. No internet required at scan time for either party.
If the attendee never opens the app while online, a fallback flow uses the device's secure enclave to generate a signed attestation that the secret key is present on the device. This is not as strong as the full rotating system, but it is still significantly more secure than a static code.
Real-World Impact
Since launching rotating QR codes, Mega Tickets has processed over 200,000 ticket scans. The results speak for themselves:
The Future of Ticketing Is Dynamic
Static QR codes were a reasonable solution when smartphones were new and event technology was primitive. But in 2026, there is no excuse for using a technology that can be defeated by a screenshot.
Rotating QR codes with cryptographic validation and GPS gating represent the new standard. They protect fans from scams, organizers from chargebacks, and the entire ecosystem from the corrosive effects of scalping and fraud.
At Mega Tickets, security is not a premium add-on. It is built into every single ticket, for every single event, at no extra cost. Because trust is the foundation of live events, and trust starts with a ticket that actually works.
All third-party trademarks referenced on this site are the property of their respective owners. As an affiliate partner of select third-party ticketing platforms, we may earn a commission from qualifying purchases made through outbound links. This does not affect the price you pay. Comparisons reflect publicly observed pricing categories as of 2026 and are illustrative only.